zizmor
Static analysis tool that finds and fixes security issues in CI/CD configurations, including GitHub Actions workflows, Dependabot, and pre-commit.
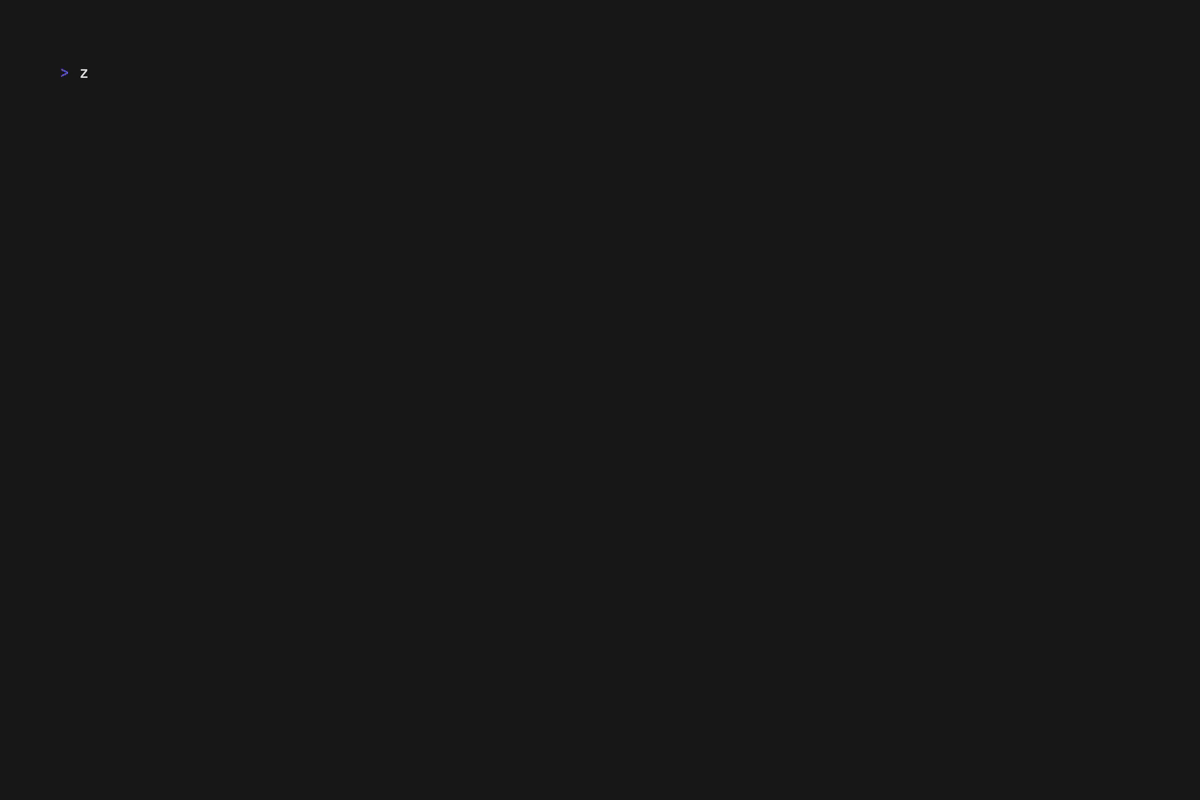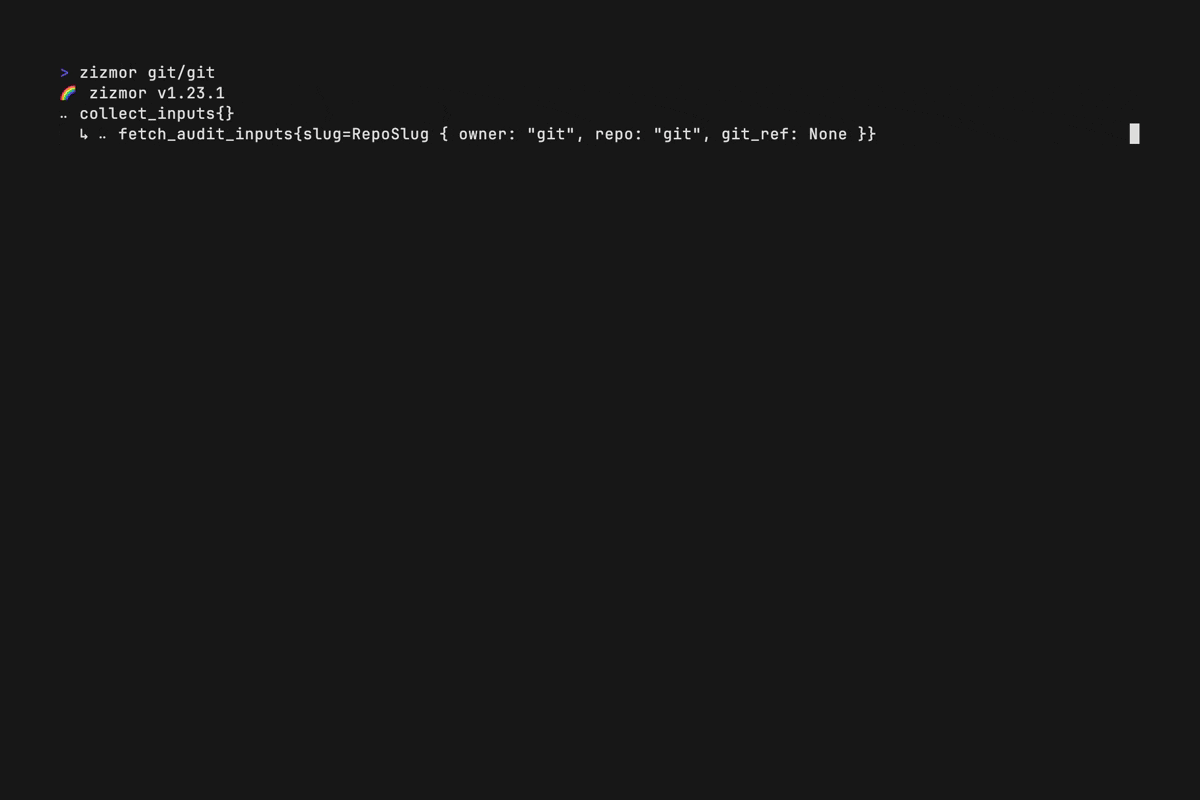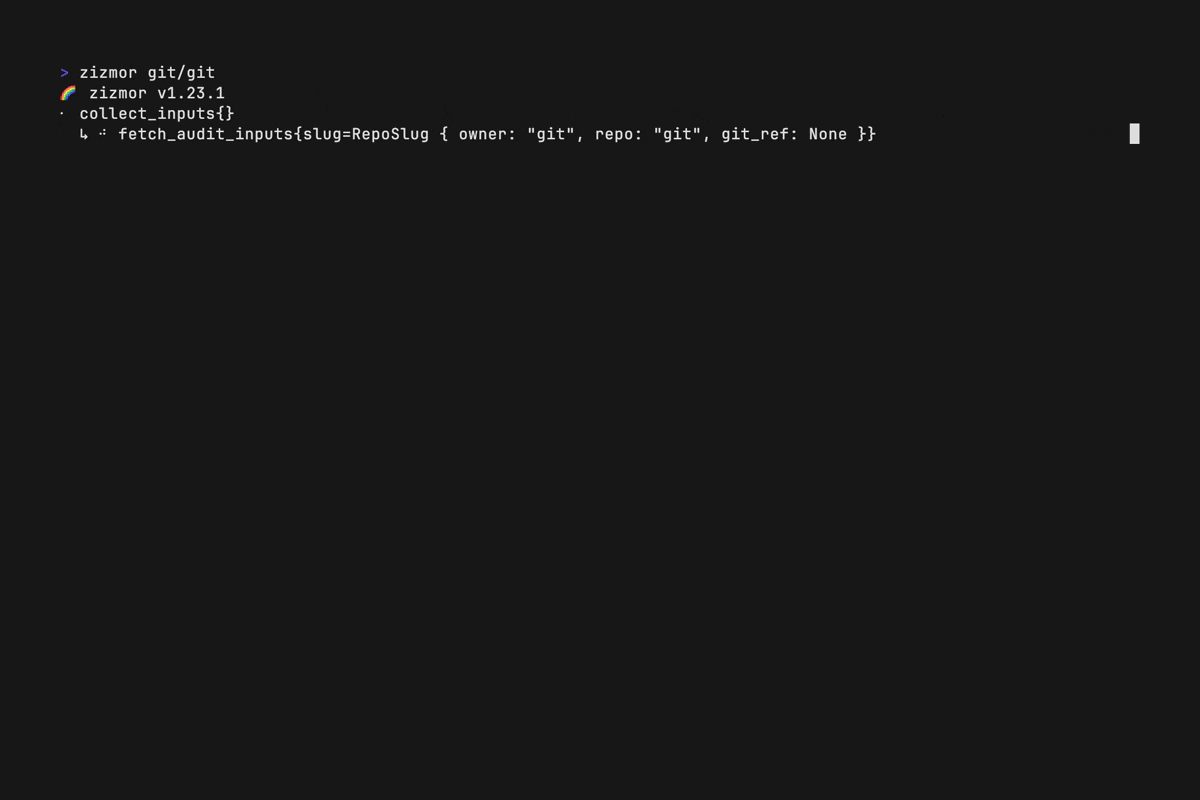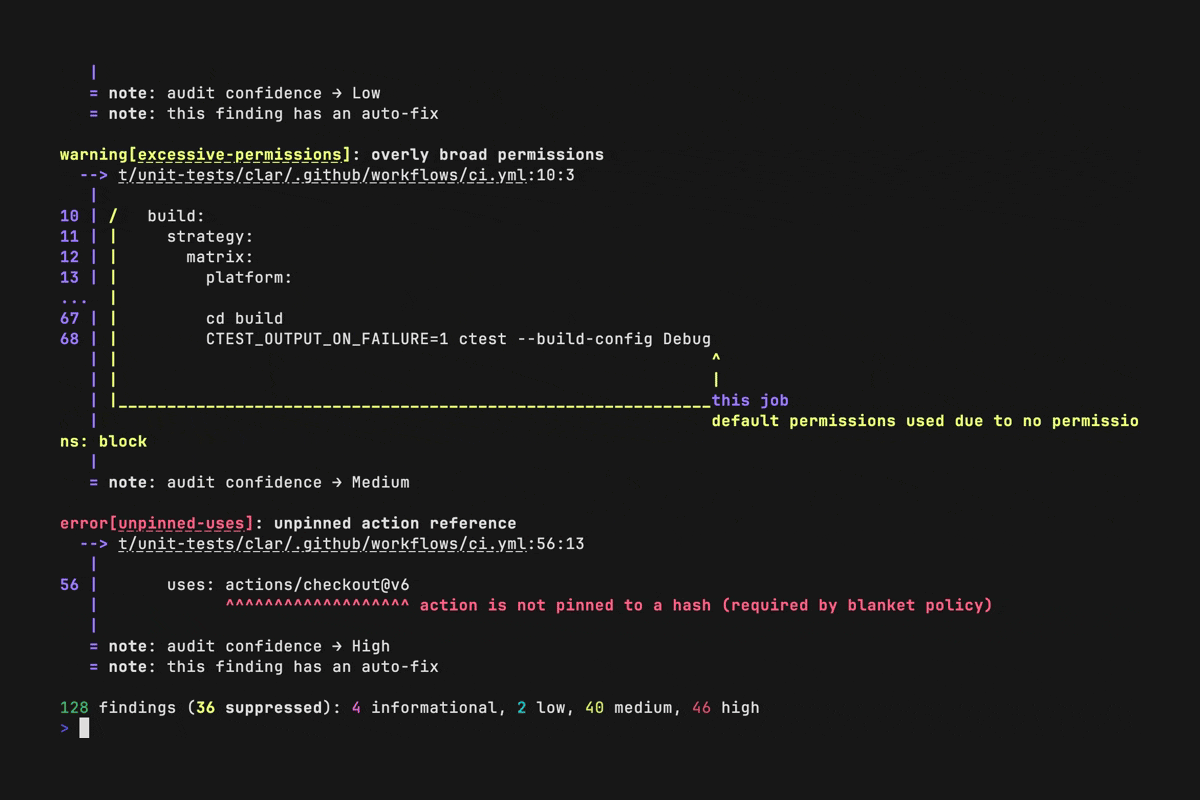
zizmor is a static analysis tool for CI/CD systems. It scans CI/CD configuration files for security problems and can fix some of them. Supported targets are GitHub Actions, Dependabot, and pre-commit setups. It is a command-line tool published on crates.io and licensed under MIT.
It reports several classes of issues: template injection vulnerabilities that can lead to attacker-controlled code execution, accidental credential persistence and leakage, excessive permission scopes and credential grants to runners, and impostor commits and confusable git references. The README says this list is partial. The full set of audits is documented at docs.zizmor.sh/audits.
The intended users are developers, security engineers, and maintainers who write or review GitHub Actions workflows and want to find security misconfigurations before they ship. The README points to the project documentation for installation steps, a quickstart, and detailed usage recipes.
Alternatives & related tools
tealdeer
Fast Rust implementation of tldr providing simplified, example-based manual pages for command-line tools
pastel
Command-line tool to generate, analyze, convert and manipulate colors across multiple formats and color spaces
jscpd
Copy/paste detector for 224 source formats with a Rust engine. Also reports dead code, complexity, git-history duplication trends, and a health score.
watchexec
File watcher that runs commands when files change, with .gitignore support and cross-platform filesystem monitoring
sd
Find and replace CLI tool with regex support, string-literal mode, and faster performance than sed
add a badge to your README
Maintain zizmor? Show that it's featured on trmn. The badge links back to this page.
[](https://www.trmn.sh/tools/zizmor?utm_source=badge)<a href="https://www.trmn.sh/tools/zizmor?utm_source=badge"><img src="https://www.trmn.sh/badge/zizmor.svg" alt="Featured on trmn" height="20"></a>