trivy
Security scanner that detects vulnerabilities, secrets, and misconfigurations in containers, filesystems, git repos, VMs, and Kubernetes
Trivy is a security scanner that identifies vulnerabilities, secrets, and configuration issues across multiple target types including container images, filesystems, Git repositories, virtual machine images, and Kubernetes clusters. The tool combines multiple scanning capabilities in a single binary: vulnerability detection (CVEs), Infrastructure as Code (IaC) misconfiguration analysis, secret detection, software license identification, and Software Bill of Materials (SBOM) generation.
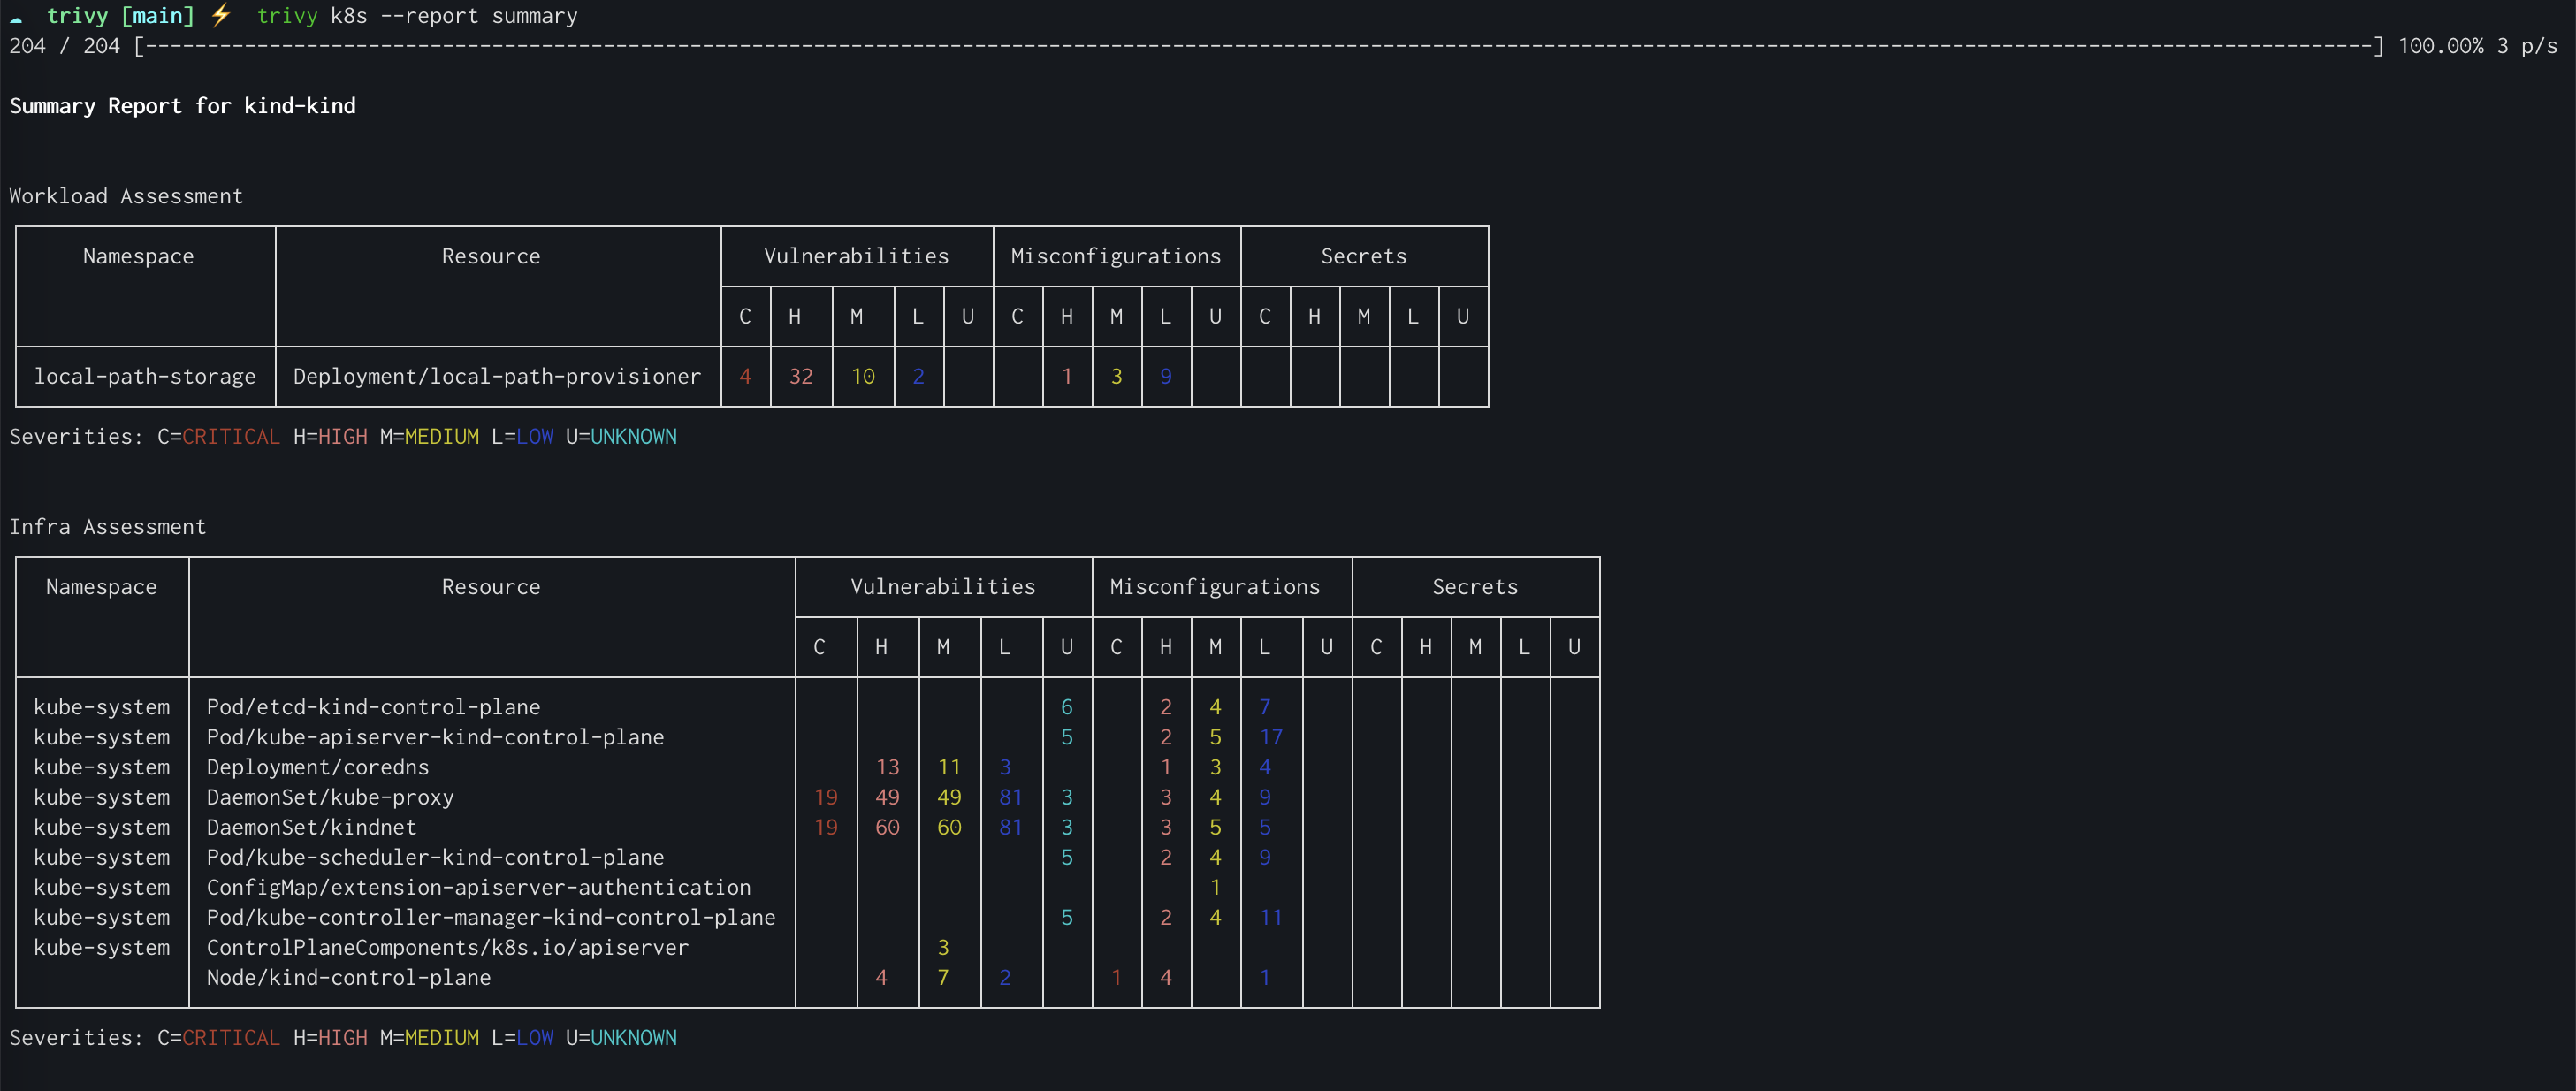
Trivy supports scanning OS packages and software dependencies across most popular programming languages and operating systems. It can be run as a standalone CLI tool with commands like trivy image python:3.4-alpine to scan container images or trivy fs --scanners vuln,secret,misconfig myproject/ to analyze local filesystems with specific scanner combinations. For Kubernetes environments, commands like trivy k8s --report summary cluster provide cluster-wide security assessment.
The tool integrates with development workflows through GitHub Actions, Kubernetes operators, and VS Code extensions. It's available as a Docker container (docker run aquasec/trivy), system packages, and standalone binaries, making it suitable for both local development security checks and CI/CD pipeline integration. Security teams and developers can use Trivy for container security scanning, infrastructure auditing, and compliance validation across their deployment pipeline.
Installation
# via Homebrew
brew install trivy
# via Docker
docker run aquasec/trivy
Alternatives & related tools
k9s
Terminal UI for managing and observing Kubernetes clusters with real-time monitoring and resource navigation
k6
JavaScript-based load testing tool for developers with HTTP, WebSockets, gRPC support and CI integration
TruffleHog
Secrets scanner that finds credentials in Git, filesystems, S3/GCS buckets and Docker images, classifies 800+ types, and verifies whether they are live.
Terraform
Infrastructure-as-code CLI that builds, changes, and versions infrastructure from declarative configuration files, using execution plans and a resource graph.
asdf
Version manager that handles multiple language runtimes per project through plugins, using a single CLI and a .tool-versions file.
add a badge to your README
Maintain trivy? Show that it's featured on trmn. The badge links back to this page.
[](https://www.trmn.sh/tools/trivy?utm_source=badge)<a href="https://www.trmn.sh/tools/trivy?utm_source=badge"><img src="https://www.trmn.sh/badge/trivy.svg" alt="Featured on trmn" height="20"></a>